Solar
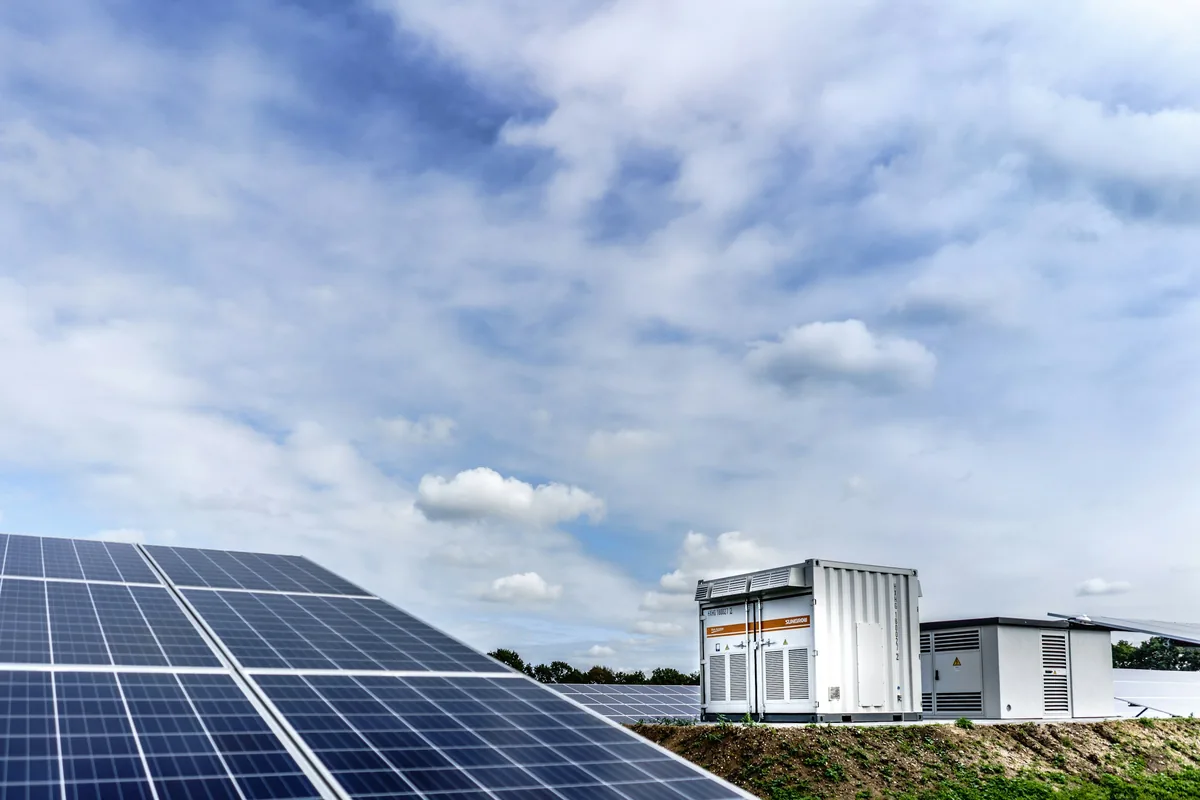
SunSpec and Sungrow inverters over read-only Modbus TCP.
GridShield collects read-only evidence from your OT and IT devices, hash-chains every record and keeps RSAW worksheets current for all 14 FERC-approved CIP standards — entirely inside your network.
Configuration screenshots captured by hand, access reviews in spreadsheets and evidence gathered in the weeks before an audit are slow to produce and hard to trust. Generic IT tools rarely speak the protocols your OT devices use, and active scanning is not welcome near protection systems.
GridShield collects that evidence continuously and read-only, from the devices themselves, and keeps it in a tamper-evident chain your auditors can verify.
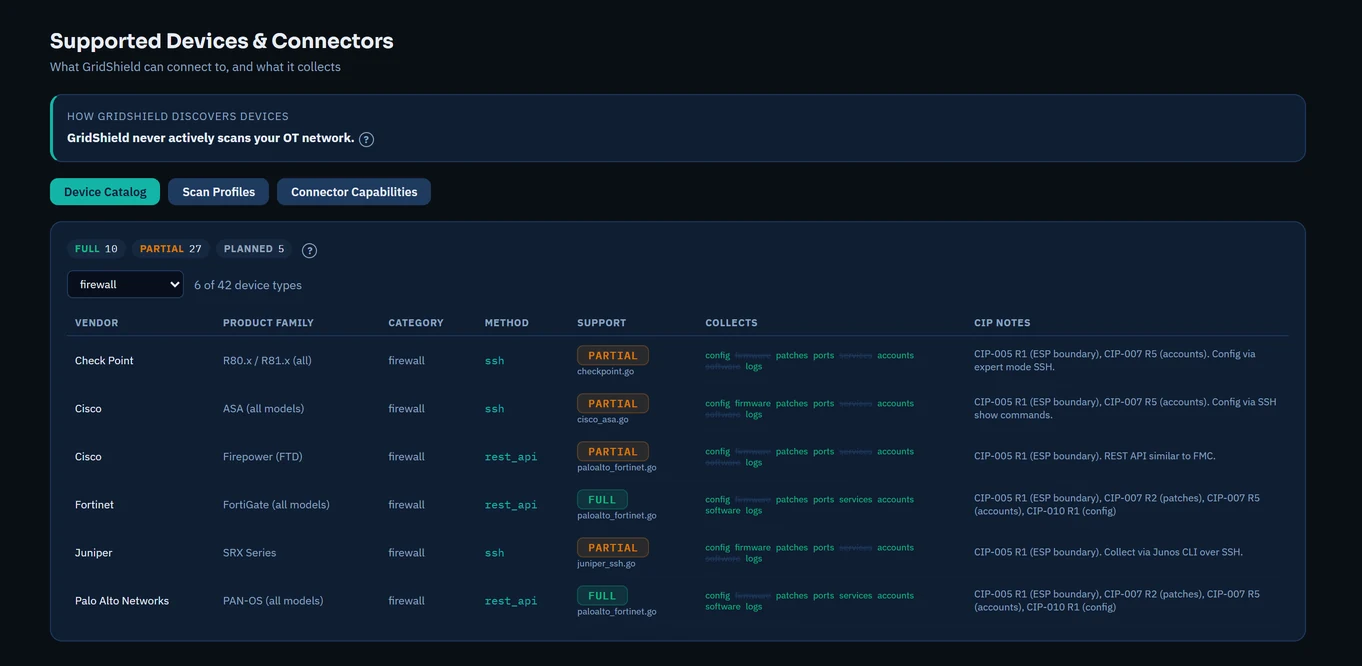
Counted from the product itself — including what is partial and what is still planned.
RSAW worksheets fill in from collected evidence, with an assessor verdict and review step.
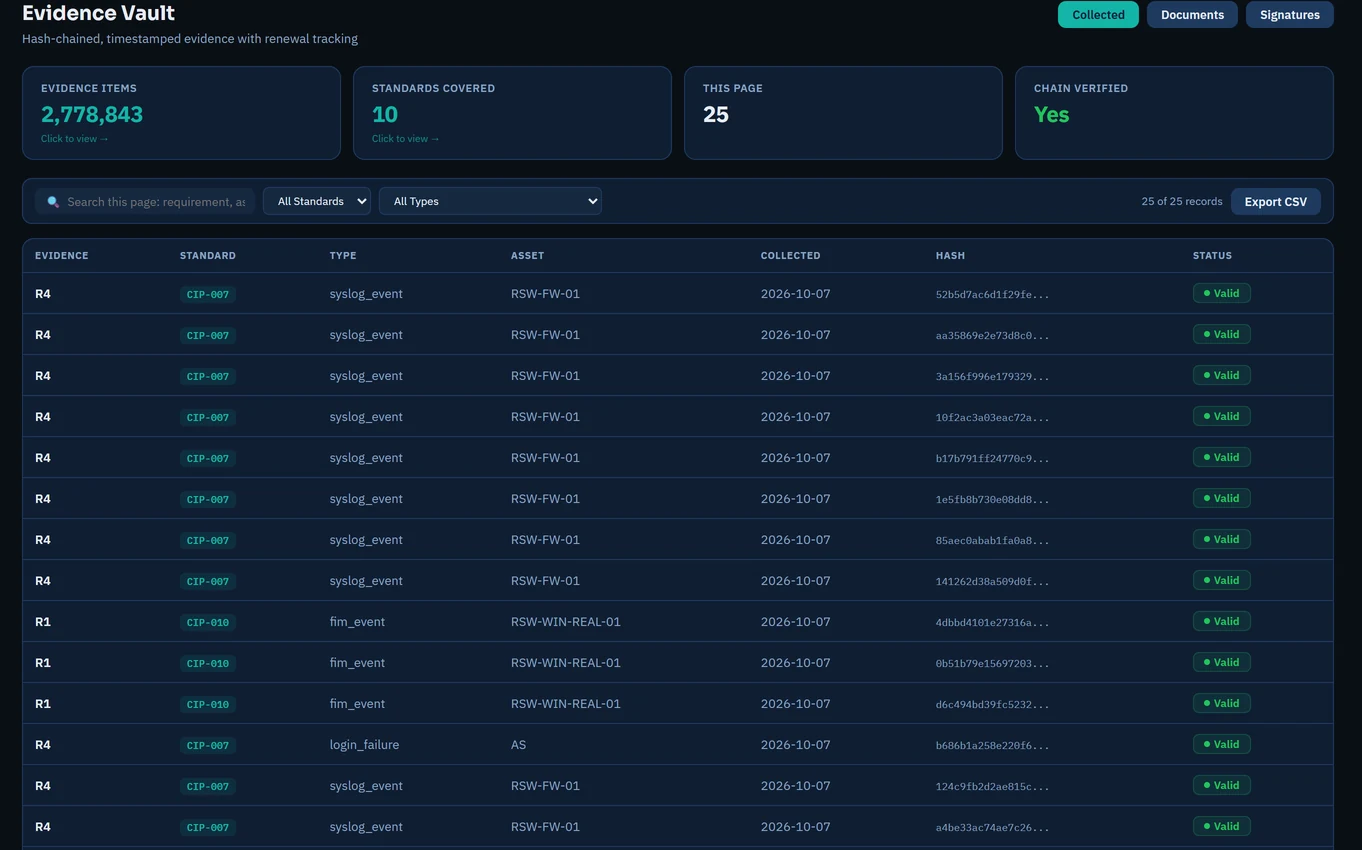
Each record is SHA-256 chained per asset; the Evidence Vault verifies the chain.
Use them together or on their own.
Read-only collection from OT and IT devices, a hash-chained Evidence Vault and RSAW worksheets — inside your network.
Learn more →Impact categorization, policies, the CIP-003 low-impact plan, records for every standard and RSAW building.
Learn more →Drafts and gap-checks CIP-003 and CIP-013 documents on a local model, with mandatory human review.
Learn more →Performance ratio, capacity factor and alarms for solar, battery storage and wind.
Learn more →Scheduled investor, O&M and CIP audit reports from your performance and compliance data.
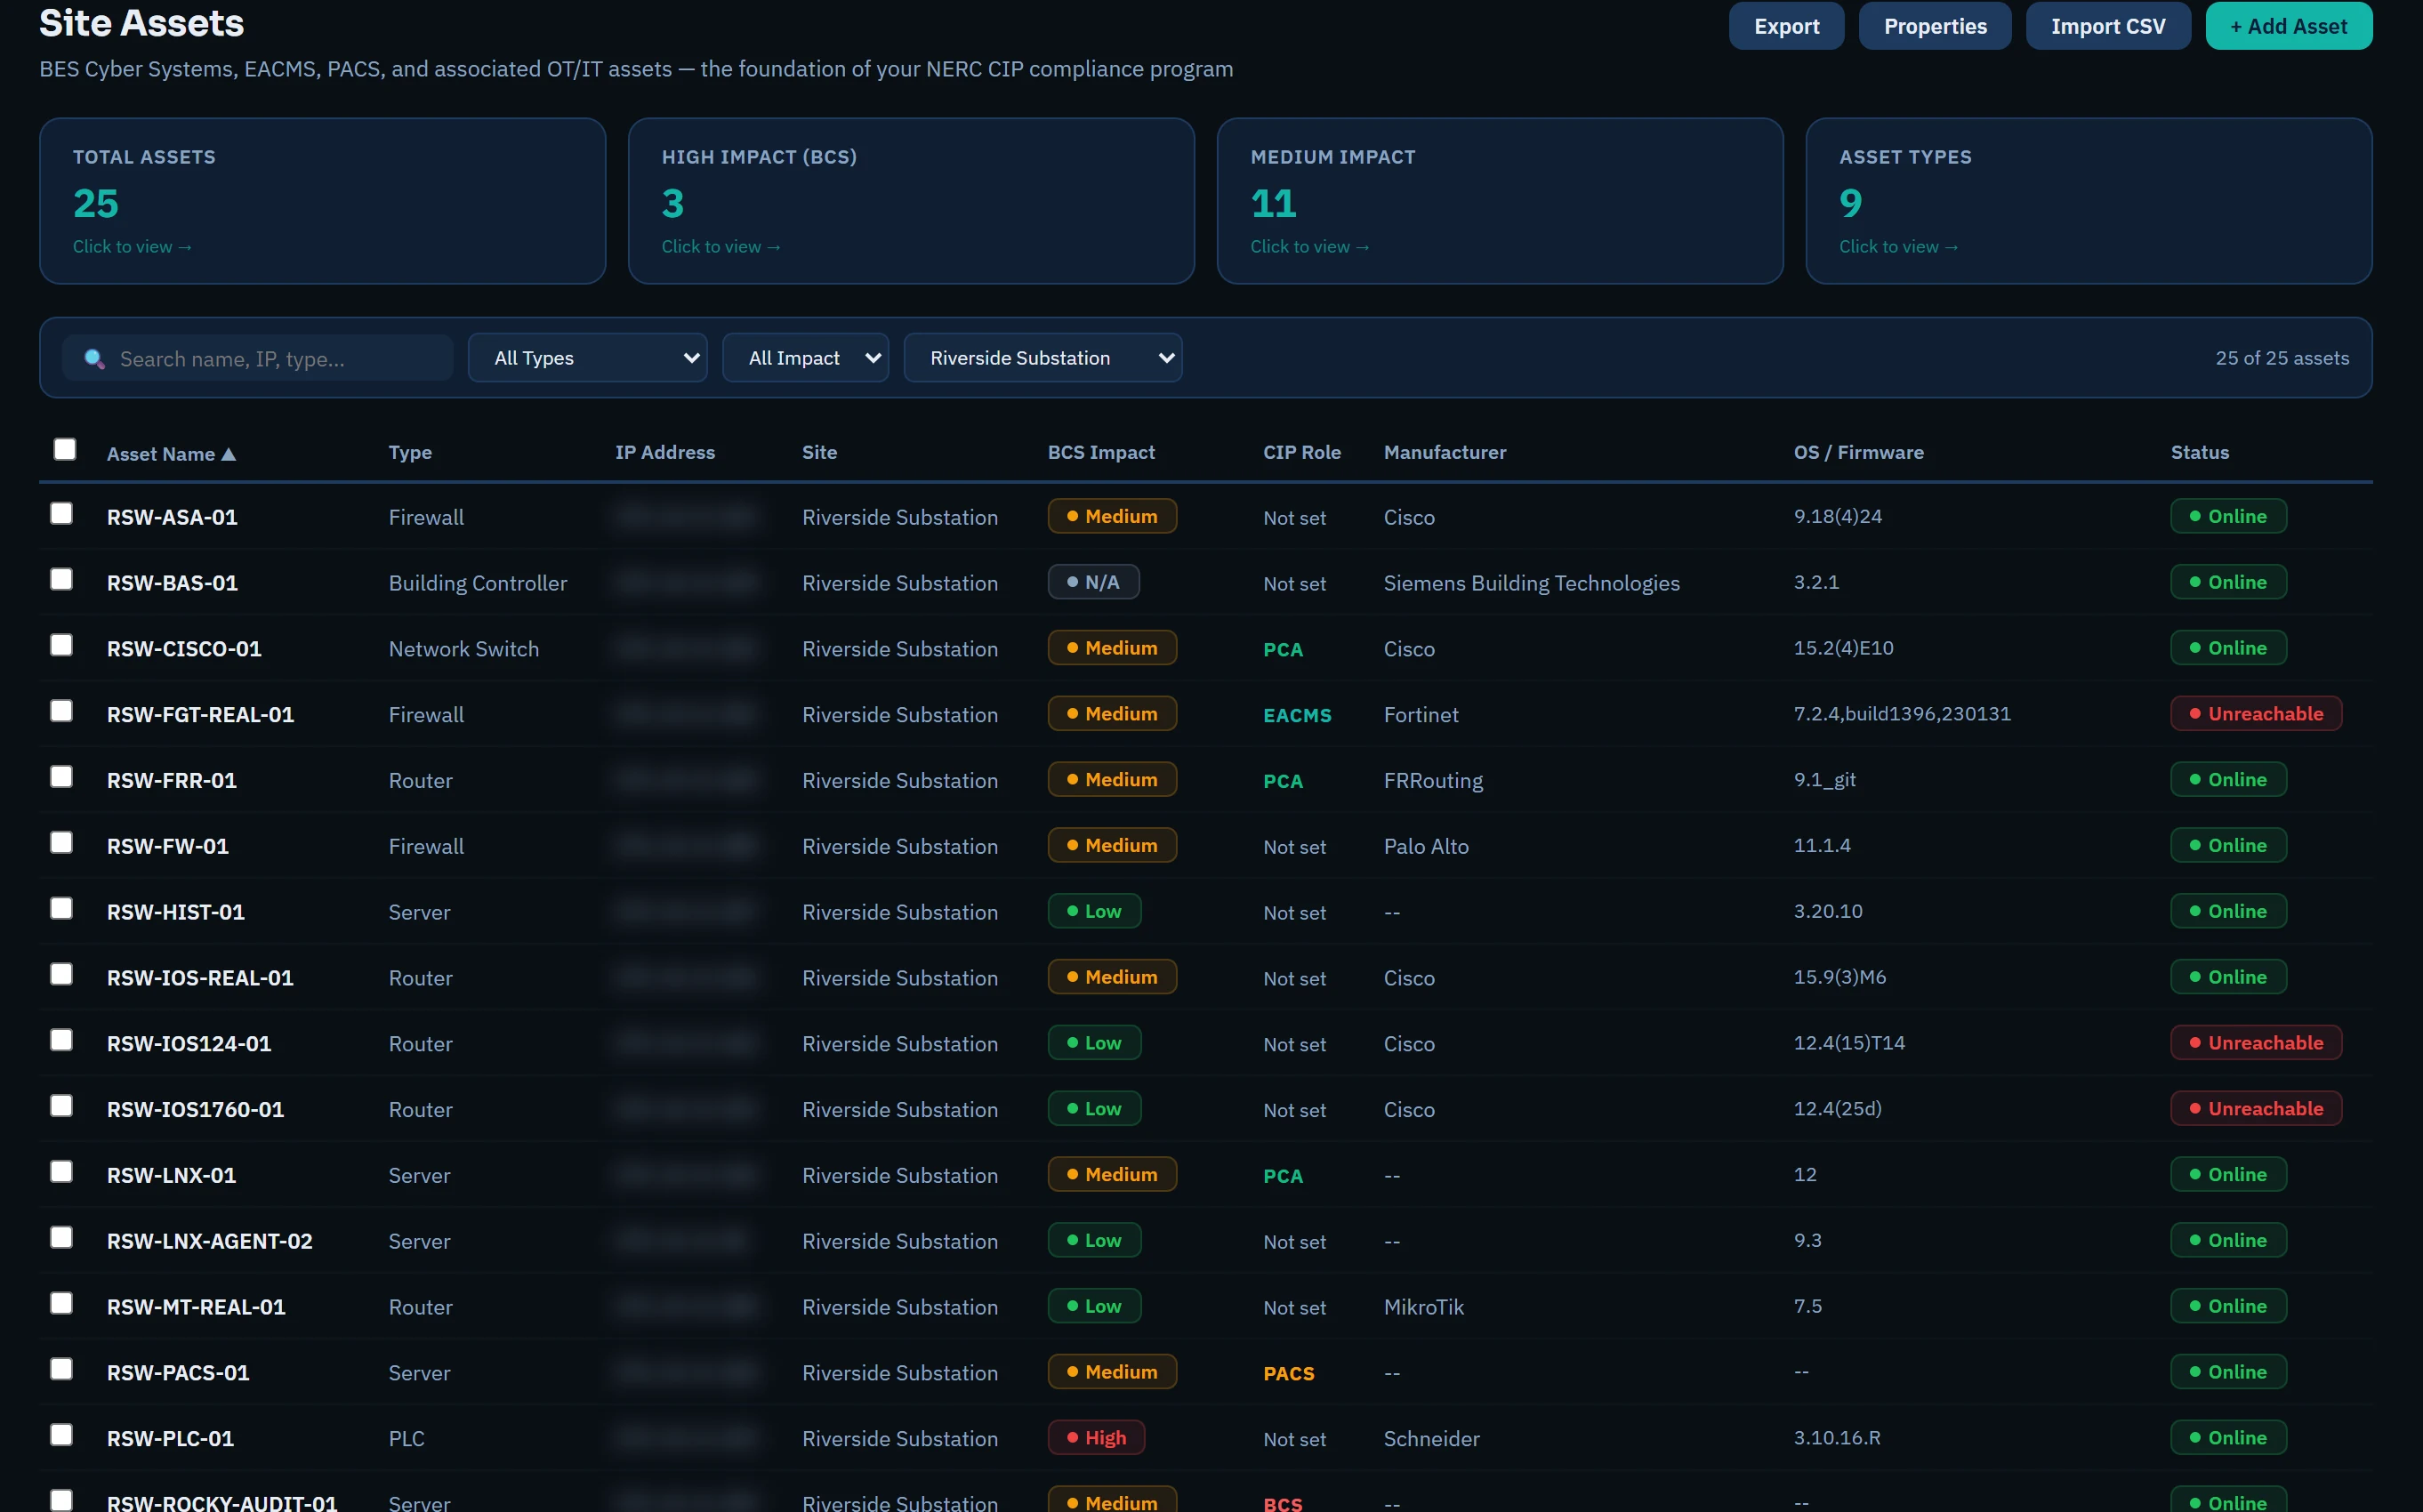
Learn more →Site Nodes poll devices with read functions only, receive syslog, SNMP traps and NetFlow, and watch SPAN traffic passively.
Every record is SHA-256 hash-chained per asset in the Evidence Vault, so any alteration is detectable.
Worksheets for all 14 FERC-approved CIP standards fill in from collected evidence, ready for your team to review.
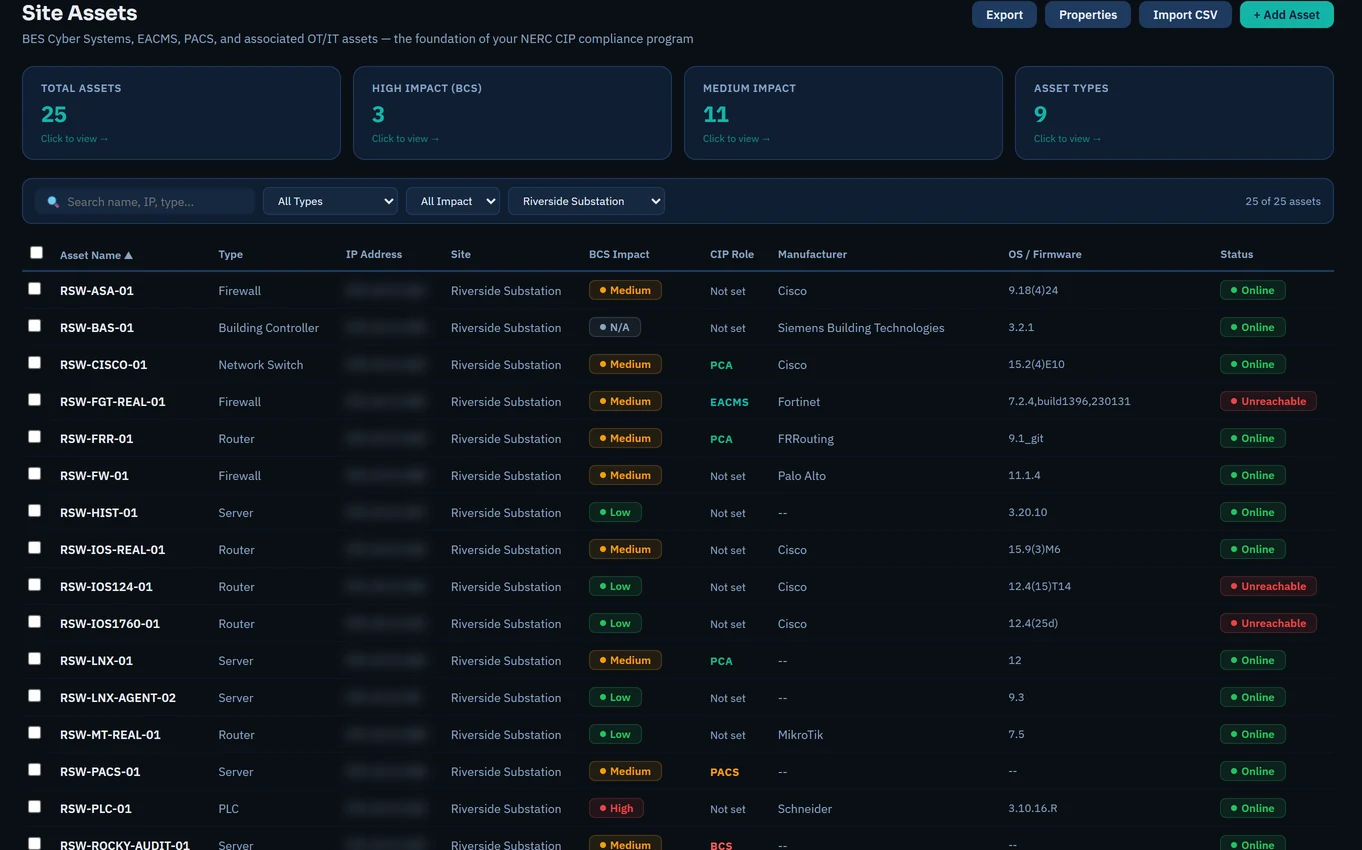
IP addresses are blurred.
SunSpec and Sungrow inverters over read-only Modbus TCP.
Read-only battery readings with state-of-charge plausibility checks.
Turbine controllers over Modbus TCP and passive IEC 61850 GOOSE monitoring.
Read-only by design
Modbus write function codes and DNP3 select/operate are blocked at the Node, so GridShield can sit beside protection systems without ever issuing a control command.
Modbus write codes and DNP3 select/operate are blocked. Nothing issues a control command.
Installs from a bootable ISO as a hardened Linux appliance and runs entirely on-premises.
Updates install only after their GridSafe Ed25519 signature verifies — nothing unsigned or altered is accepted.
A built-in certificate authority issues the certificates Nodes and Agents use.
In the U.S., monitoring inside the electronic security perimeter: Control Centers from October 1, 2028, other medium-impact systems with ERC by October 1, 2030 — time to plan the sensors now.
Revised NERC registration criteria bring many solar, wind and BESS sites into scope — mostly at low impact.
Documented plans for awareness, access, incident response and transient devices still need evidence.
NERC CIP is built in. In the EU, UK, Australia, Saudi Arabia and India the same evidence lines up with your rules — choose your region to see what applies and what GridSafe does for you.