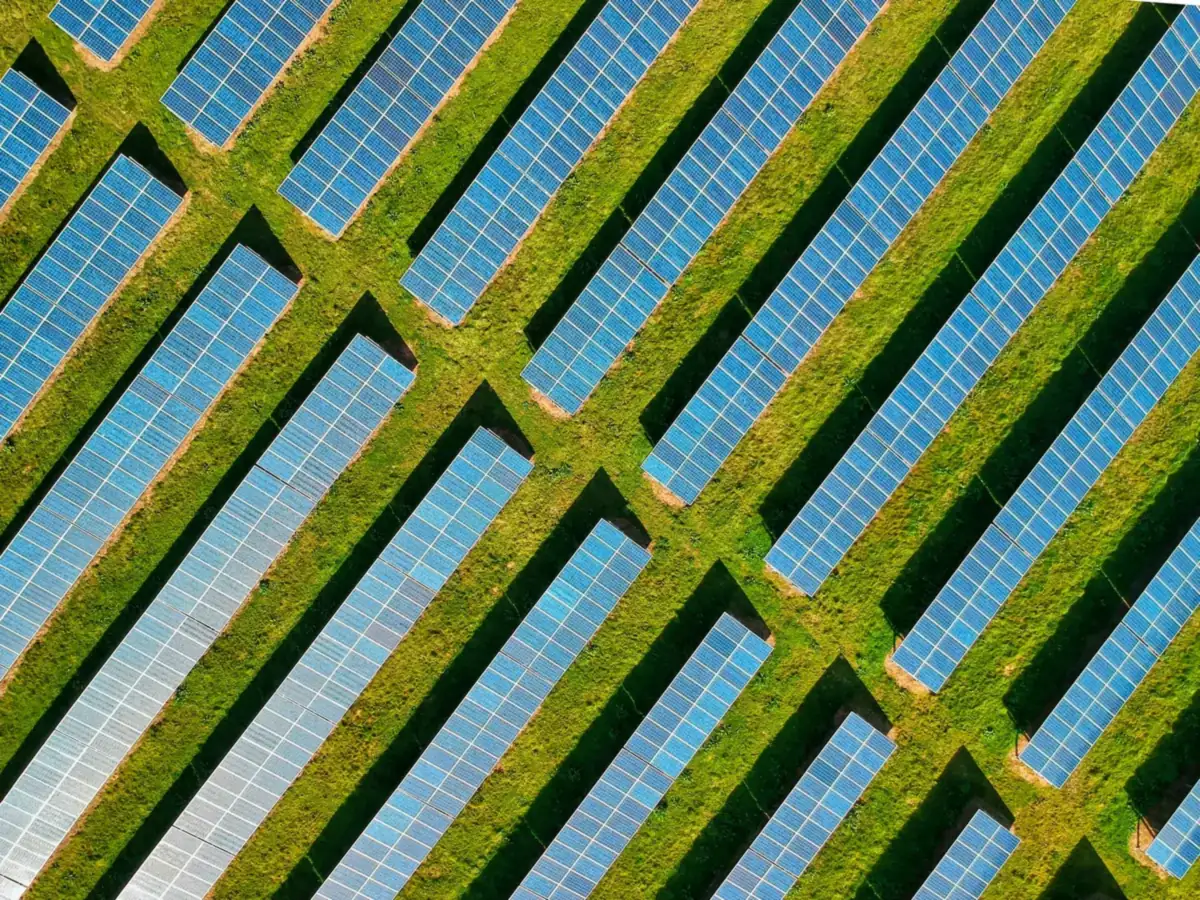
Solar
Inverter telemetry from SunSpec-compliant and Sungrow inverters over read-only Modbus TCP, alongside the network, firewall and host evidence your plant's CIP program needs.
Solar, battery storage, wind, substations, control centers and thermal plants each run different equipment. GridShield collects from it read-only and turns it into NERC CIP evidence.
What GridShield collects at each kind of facility — stated as it is today.
Inverter telemetry from SunSpec-compliant and Sungrow inverters over read-only Modbus TCP, alongside the network, firewall and host evidence your plant's CIP program needs.
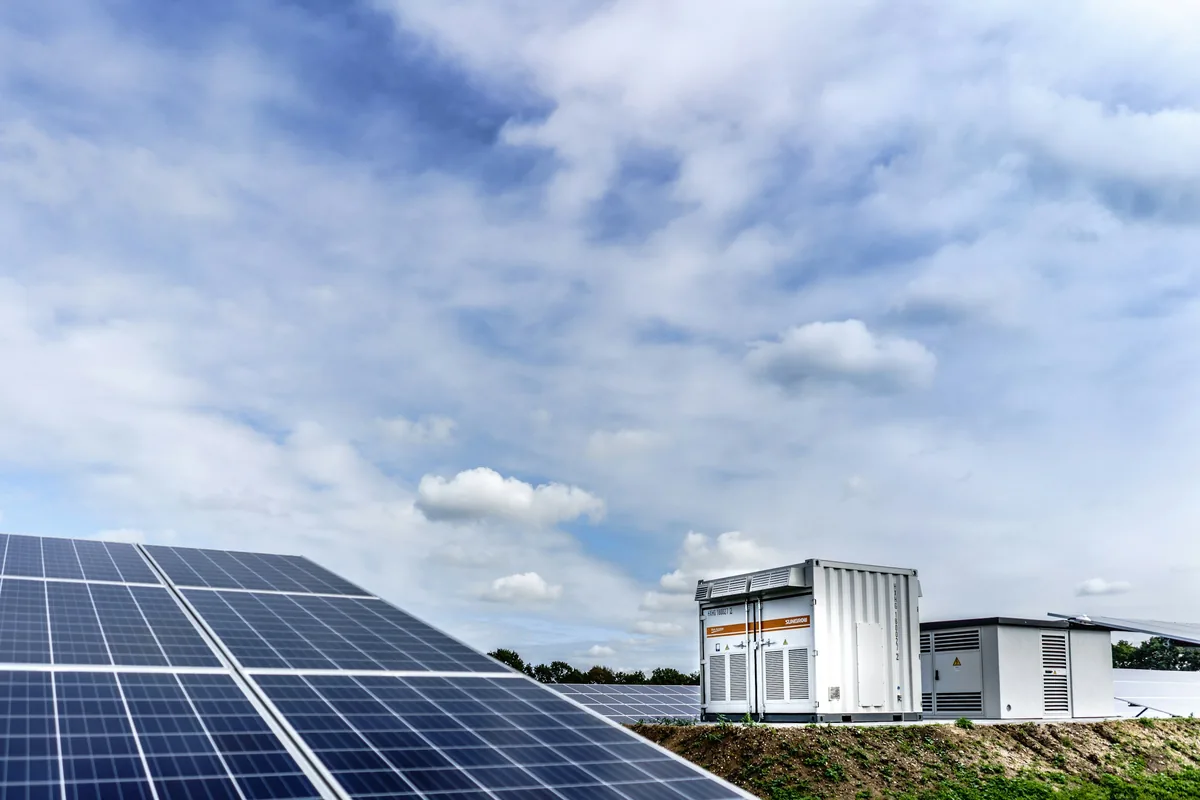
Battery system readings collected read-only, with state-of-charge plausibility checks that flag readings that cannot be physically right.
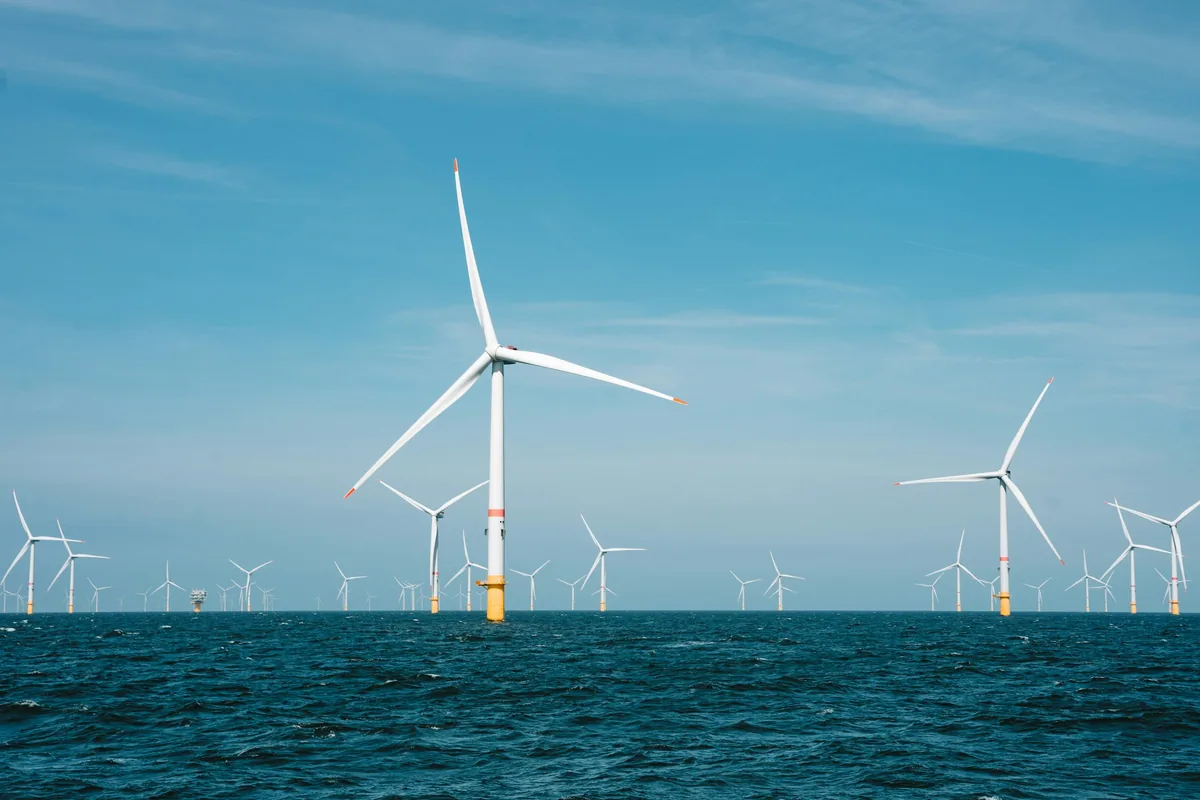
Turbine controller registers over read-only Modbus TCP, plus passive IEC 61850 GOOSE monitoring on a SPAN port for replayed or unexpected messages.
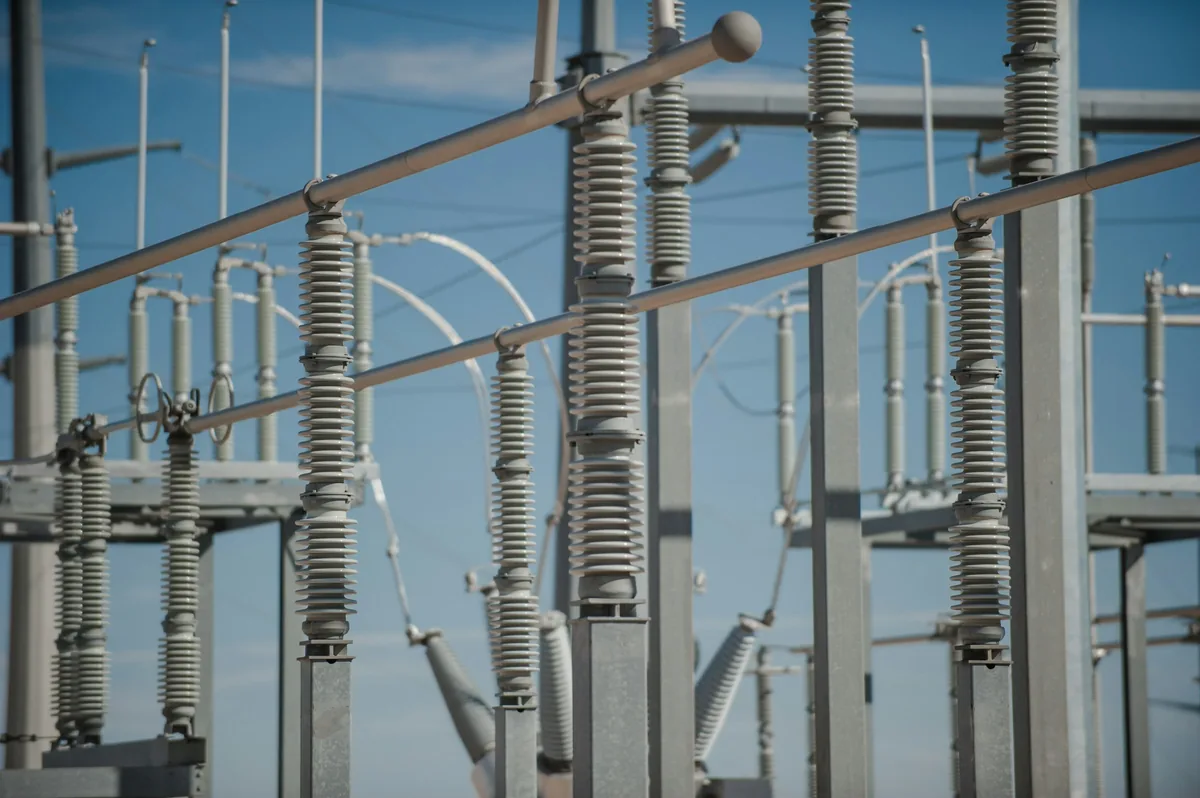
SEL relays, DNP3 RTUs (read-only polling), IEC 61850 GOOSE on SPAN, and the firewalls, switches and routers that form your electronic security perimeter.
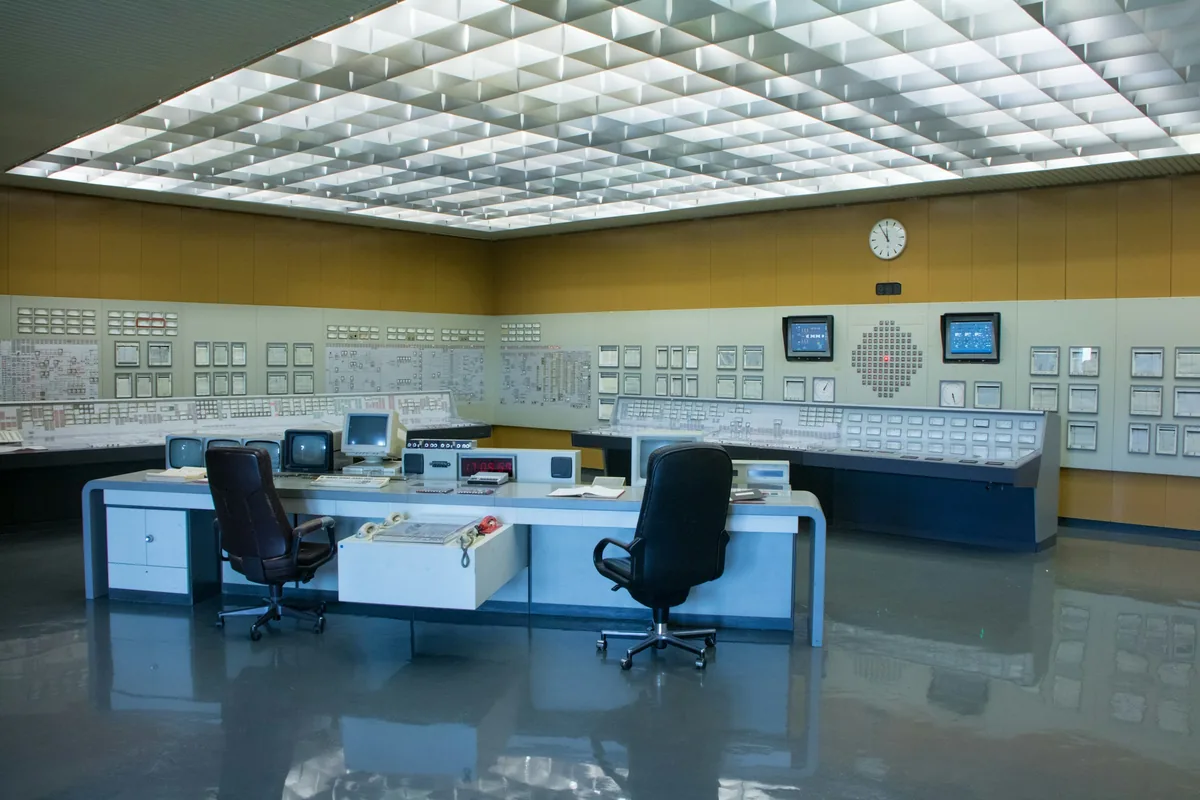
Windows and Linux hosts over WinRM and SSH, optional Agents for file-integrity monitoring, and Active Directory accounts for access evidence.
PLC, protection-relay and network-device evidence over Modbus TCP, DNP3, SEL and SNMP — read-only throughout.
Each has a native connector. The product's device catalog shows, per model, whether support is full or partial and exactly which evidence is collected.
Product names are trademarks of their owners and indicate compatibility, not endorsement.
In the U.S., requires monitoring of network activity inside the electronic security perimeter — at Control Centers and backup Control Centers from October 1, 2028, and for other medium-impact systems with External Routable Connectivity by October 1, 2030 — with retention and protection of that data. GridShield's passive SPAN capture and evidence vault support it.
NERC's revised registration criteria bring many inverter-based resources into registration for the first time. Most newly registered sites categorize as low impact, which means CIP-003 obligations — exactly where structured, repeatable evidence helps.
Low-impact sites still need documented plans for cyber security awareness, physical and electronic access, incident response and transient devices. GridShield and CIPStart keep that evidence organized and current.
GridShield is built around NERC CIP. It also maps CIP evidence to NIST CSF and IEC 62443 references for teams that report against more than one framework.